Privacy officers
EDFlow for privacy officers: the audit log and what is logged, per-patient access reports, monitoring alerts A-1 to A-28, exports with second-person approval, incidents, emergency revoke and safety concerns.
The privacy officer role holds the custodian's audit and investigation tools. It can't be combined with the manager role or any clinical role.
The audit log
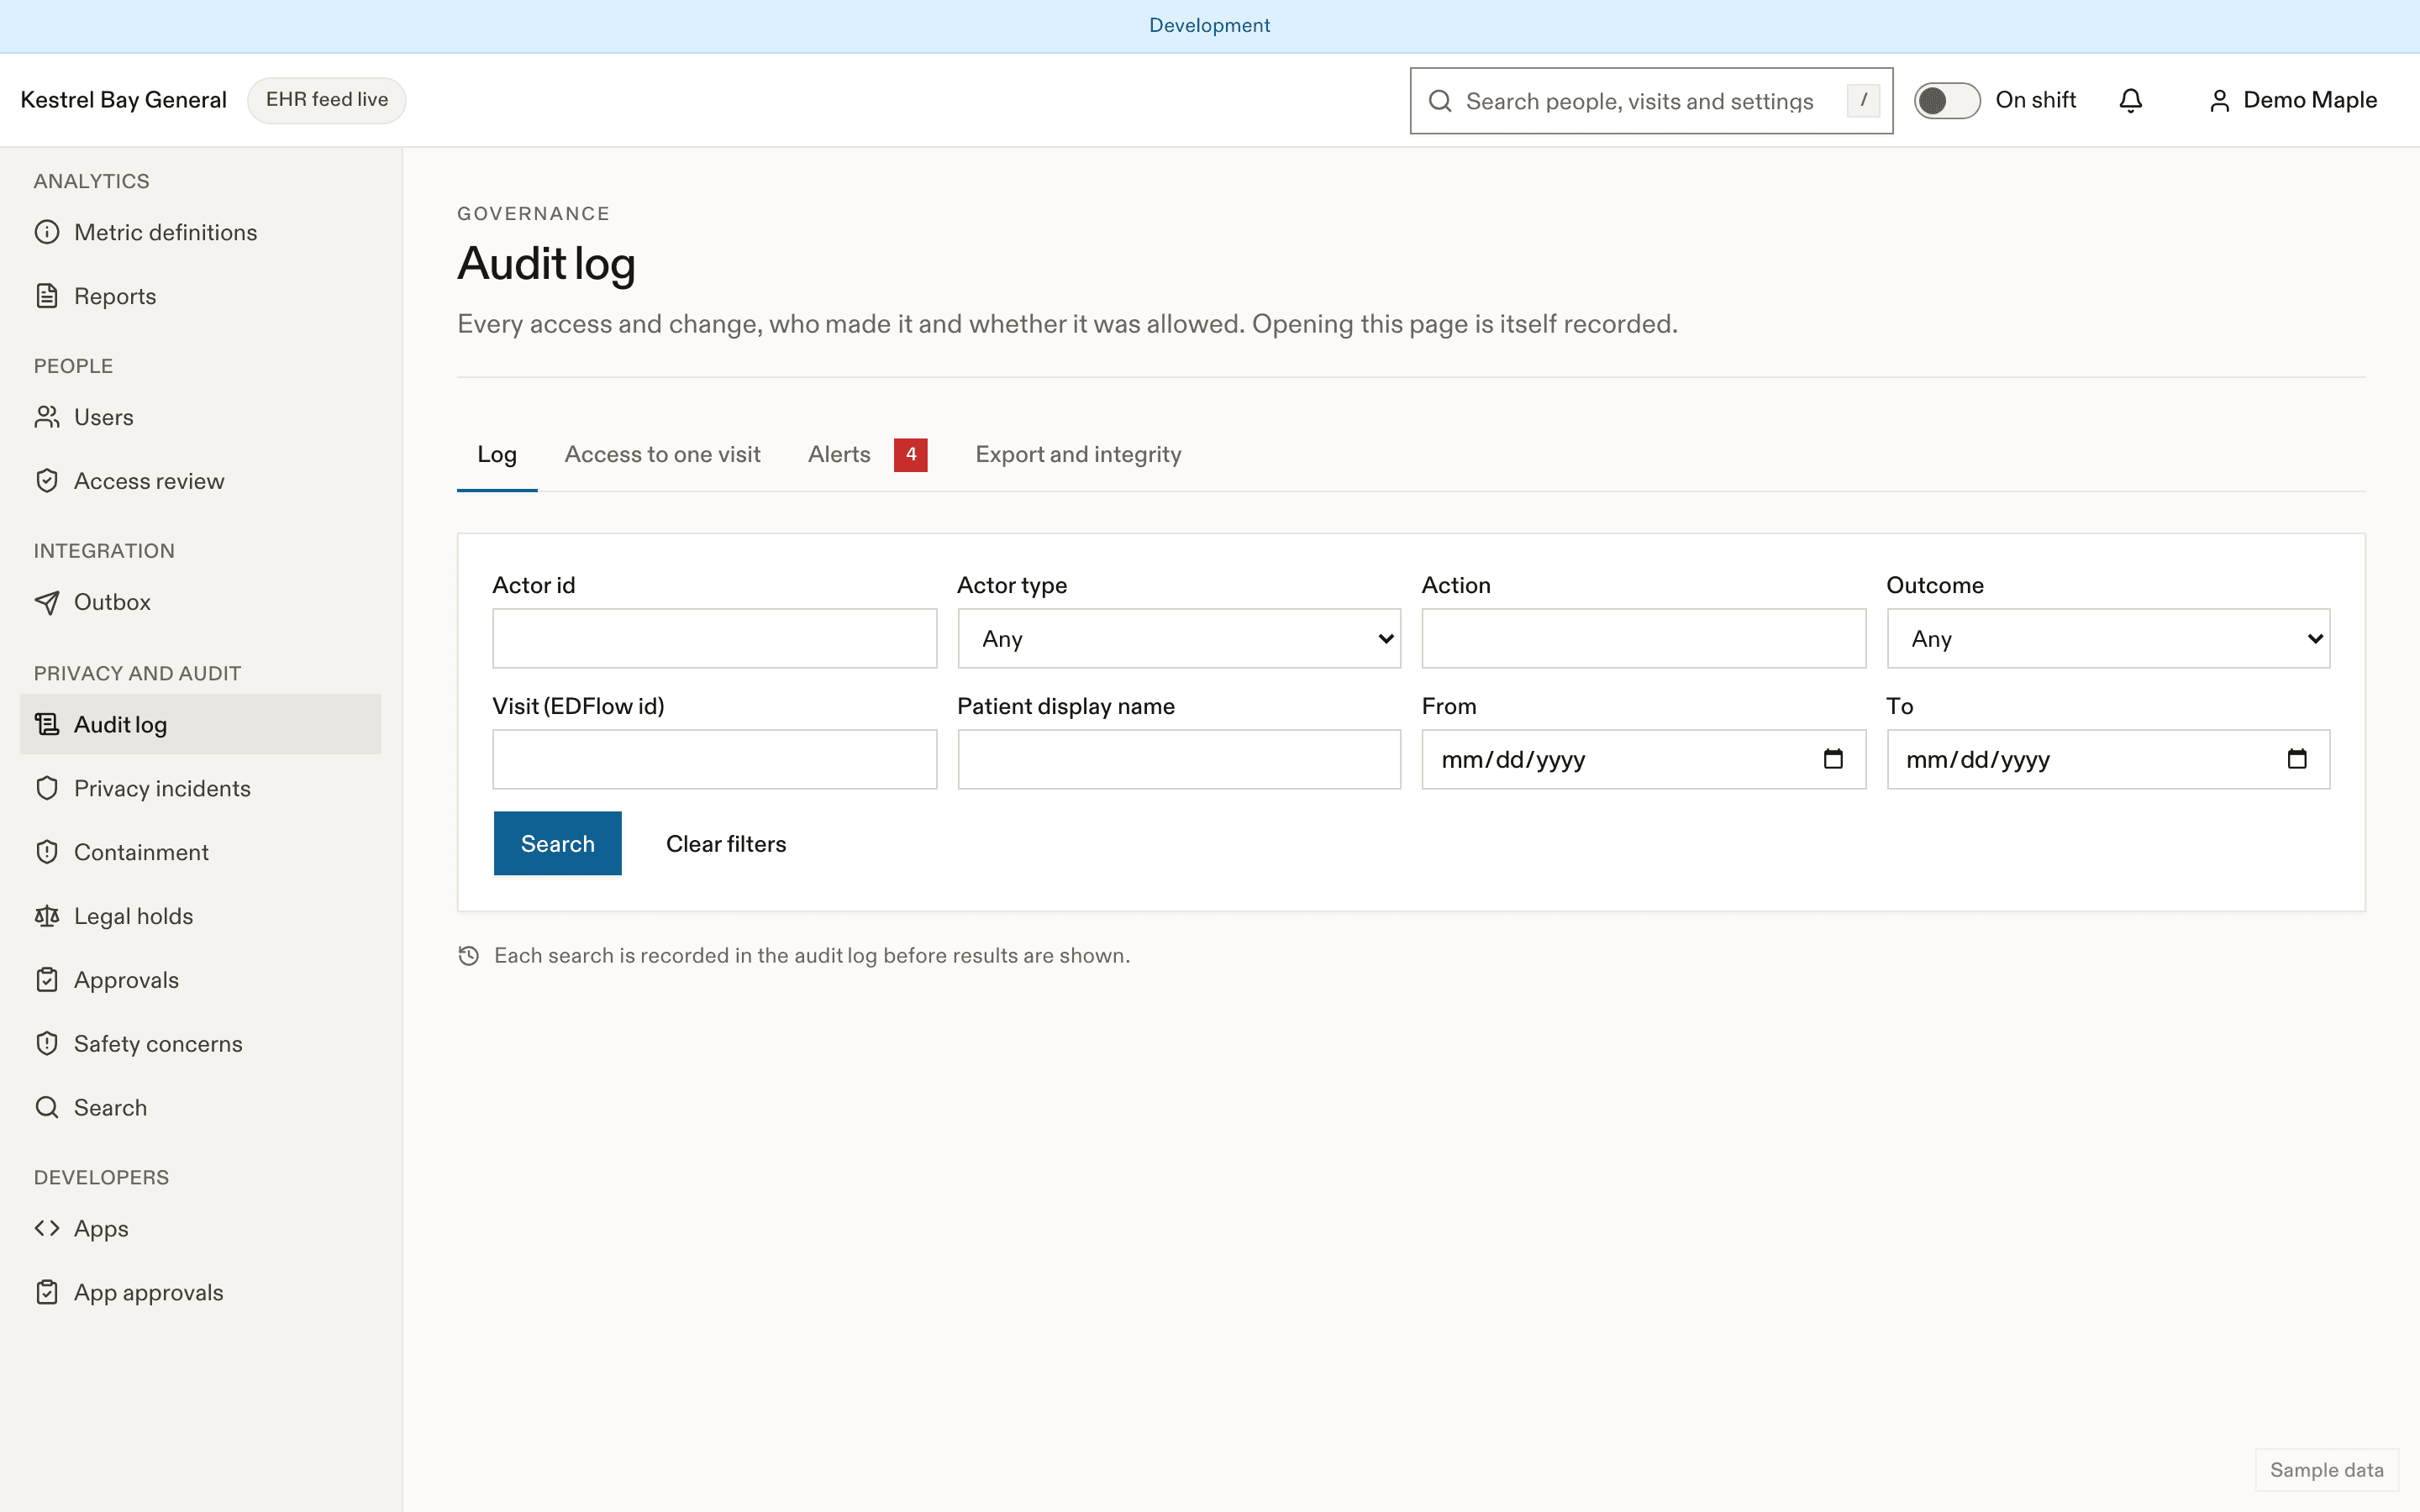
Filter by actor, actor type (patient, family, staff, station, system, integration, platform), action, visit, date range and outcome. Privacy officers can also search a visit by display name. Each row opens a detail drawer.
What is logged
| Group | Examples |
|---|---|
| Patient and family access | Sessions created and ended, rejected tokens, failed sign-ins, identity confirmed or mismatched, family links created, opened, revoked |
| Staff authentication | Sign-ins, failures, lockouts, MFA changes, password resets, SSO rejections |
| Staff access to patient data | Board views (every 15 min), each patient opened (with the tab), unmasks with reasons, card issuing and pairing approvals, payload reveals |
| State changes | Every manual action, override, result hold and release, request action, call-back, summary publication, flag change, updates pause |
| Department | Codes called, notices posted and ended, volume changes |
| Administration | Settings changes with before and after, invites, role changes, approvals, stations, content status, access reviews |
| Integration and API | Sources, key reveals, dead-letter replays, apps, credentials, scopes |
| Privacy and platform | Audit views and exports, retention runs, legal holds, incidents, emergency revokes, support access |
| AI | Safety conversations opened, automatic alerts, governance gates, kill switch |
Audit rows never contain names, tokens, phone numbers, emails, message bodies or free text. The log is append-only and each day is hashed and chained to the previous day, so tampering can be detected; exports include the digests.
Per-patient access report
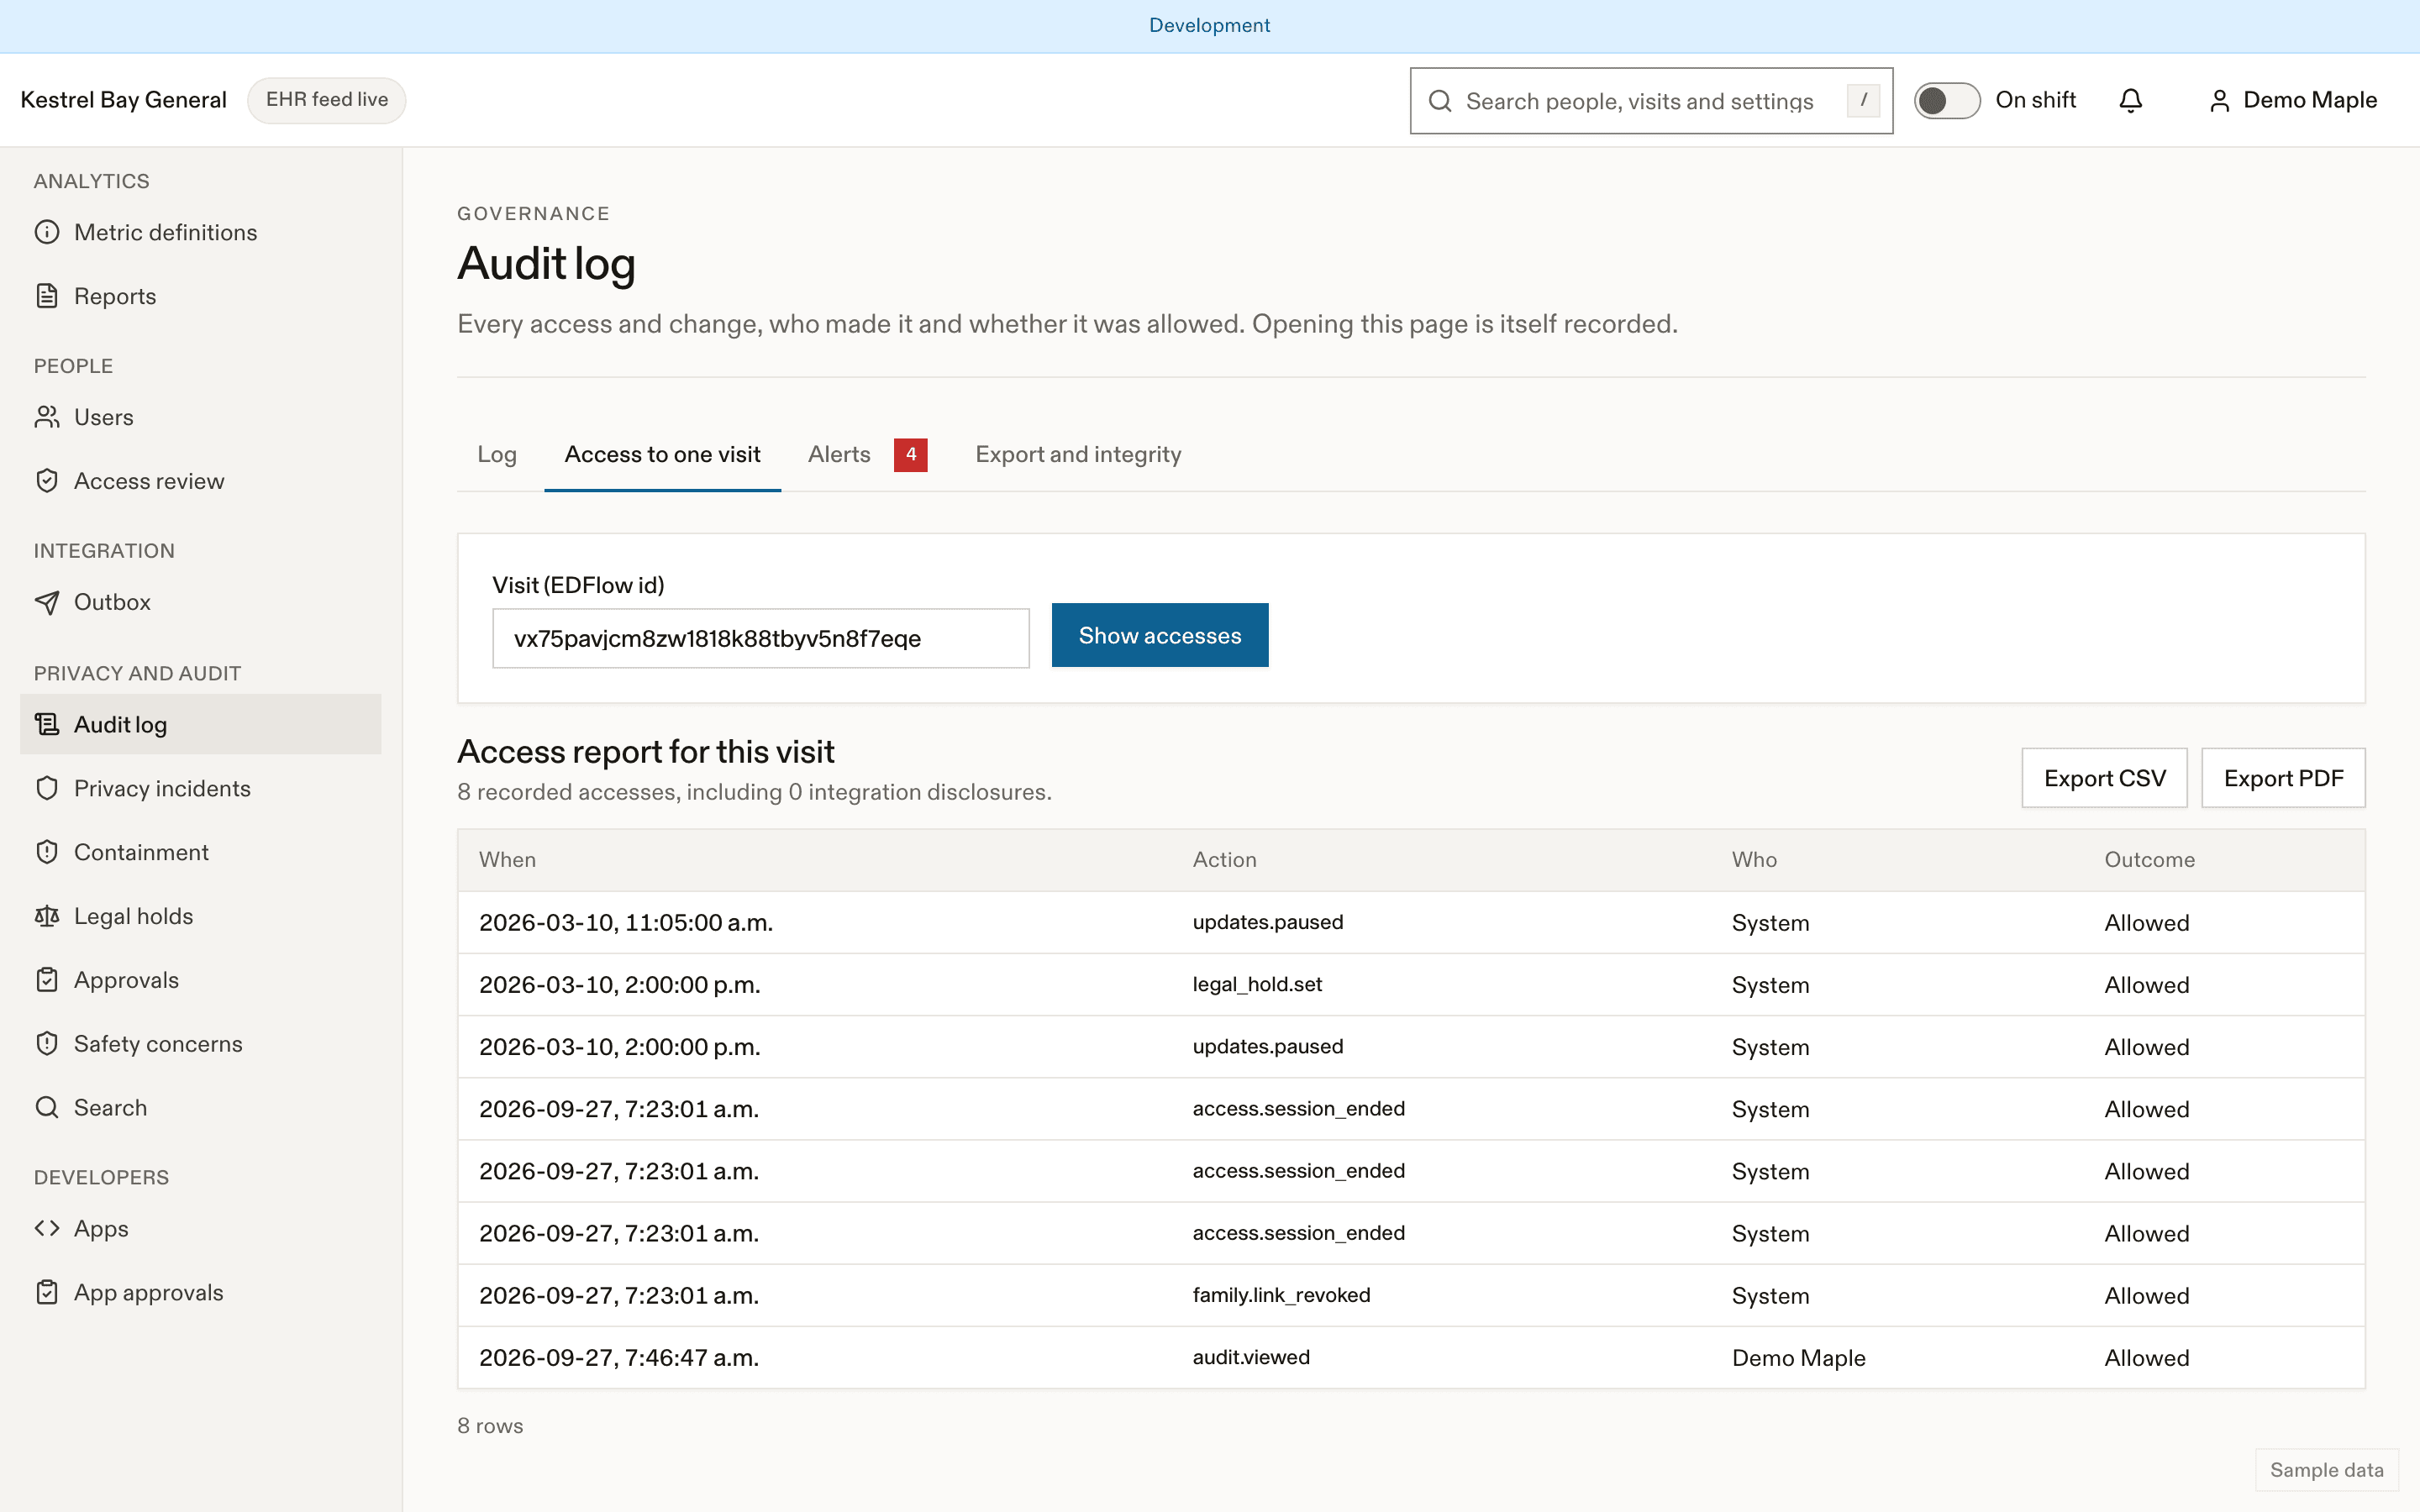
Every access to one visit, as CSV or PDF, including every integration that received the visit's data.
Monitoring alerts
Automatic rules raise alerts on this page and by email to the privacy office. Acknowledge each with a note. Examples:
| Rule | Condition |
|---|---|
| A-1 | One user opens more than 30 patients (or issues credentials, probes duplicates or reveals payloads for that many) in an hour |
| A-2 | A confidential visit opened by someone not on its care team |
| A-3 | More than 3 unmasks by one user in 12 hours |
| A-4 | 10 or more failed manual sign-ins against one visit in 24 hours |
| A-7 | An audit export |
| A-8 | Support access started |
| A-16 | A privileged role requested or activated |
| A-17 | Self-assignment to a confidential visit, or a confidential or sharing flag cleared |
| A-19 | A patient-facing trust anchor changed |
| A-23 | An integration reading far more visits than usual |
Exports
Audit exports need a second privacy officer's approval (and are themselves audited). SIEM export is available on request as CSV or NDJSON, with scheduled delivery in a later release.
Incidents and emergency revoke
Privacy incidents track a suspected breach: summary (no personal information), scope (criteria that find affected visits and place legal holds automatically), matching visit numbers from an EHR extract (hashed in memory), a notification timeline for the custodian, individuals and the IPC, the reportable decision, and closing. Anyone who is a subject or actor of the incident can't act on it. Annual statistics by IPC category are ready for the March 1 report.
Emergency revoke ends family links, patient sessions, visit credentials, or all patient and family access across the site, with a reason and the typed site name. Staff sessions are not affected.
Safety concerns
Staff report safety concerns from the console. They appear on Safety concerns with their category and status, and export to the hospital's incident system.
Related
Dernière mise à jour le
Cette page vous a-t-elle été utile?
EDFlow Mail
EDFlow Mail for the company team: shared mailboxes, AI triage of every inbound email, rules, hybrid search, support tickets with auto-acknowledgement, and the rule that mail never carries patient health information.
Access requests and retention
Answer PHIPA access requests with a EDFlow visit-record export, place and lift legal holds, and understand the retention schedule, care records and de-identification after the operational window.